
Built by engineers,
not by a sales floor.
AWJ Tech is a technology and security firm based in Dubai. We build, secure and run the systems that businesses depend on. The person who scopes your work is the person who does it, and they will tell you when you do not need something.
Leadership experience
Across IT, cybersecurity and business automation.
Security assessments
Banking, logistics, healthcare and government.
Certifications supported
ISO 27001, NESA, PCI DSS and more.
Office Locations
Serving clients across the UAE and beyond.
Good technology advice is harder to buy than it should be.
Most companies do not have a technology problem. They have a clarity problem. They are sold tools they do not need, reports they cannot act on, and projects that arrive late and half finished.
We started AWJ Tech to work the other way round. We look at what the business is actually trying to do, then build only what supports it. If the honest answer is that you do not need us, that is the answer you get.
That approach has kept clients with us past the first contract, which is the only measure of this work that matters.
Sadiq Panjwani
With over 25 years of experience across IT, cybersecurity, and business automation, Sadiq helps businesses solve complex technology challenges with practical, future-ready solutions.
From securing your systems to automating your operations, he brings the right technology, strategy, and expertise together to help your business move forward.
A hands-on leader and trusted technology partner, Sadiq focuses on solutions that create real business value, not unnecessary complexity.
Experience
25+ Years of experience across technology and business.
Expertise
Technology, engineering, automation, and business solutions.
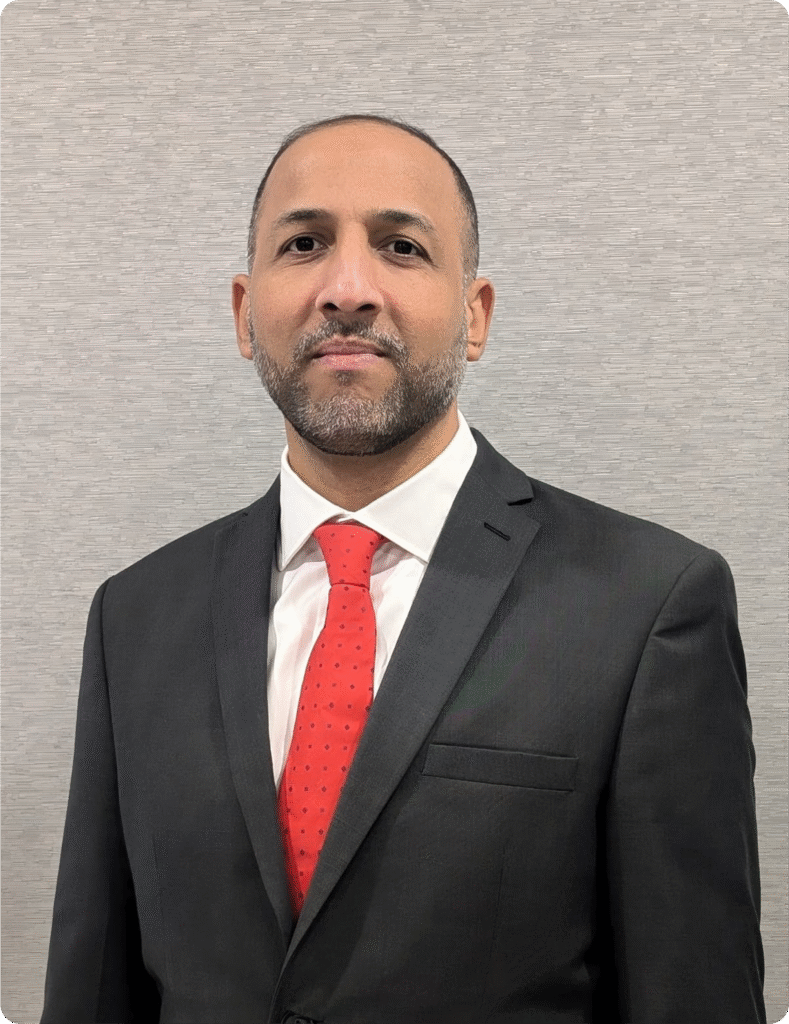
Founder & CEO – Awj Tech
Six reasons clients stay with us
post their first engagement
01
Built around you
No generic packages. We focus on what your business actually needs.
A team you can trust
Experienced people who understand technology and business.
02
A practical approach
We focus on solutions that work in the real world.
03
04
Security first
Protecting your systems, data, and people is part of everything we do.
From idea to delivery
We help you plan, implement, and improve without unnecessary complexity.
05
Built for what's next
Technology changes quickly. Your solutions should be ready for it.
06
Six things we do not compromise on.
We build around you.
You get experienced people
We keep it practical
Security comes first
It is part of everything we build, not a phase at the end.
We finish what we start
We build for what comes next
Solutions We Implement
Based in Dubai.
Working across the region.
Our head office is in Port Saeed, Dubai, and most of our clients are in the UAE. We support engagements across the wider Gulf, and United States. Testing and monitoring work is delivered remotely, and we come on site when the work needs it.
Web Applications
We test web applications for weaknesses that could expose sensitive data, bypass controls or give attackers unauthorised access.
04
Thick Clients (Smart Applications)
We assess desktop and smart applications for vulnerabilities in application logic, local data, communication and authentication mechanisms.
05
Perimeter Network and Wi-Fi
06
Cloud Security (AWS, Azure, GCP)
07
ICS / SCADA Industrial Systems
08
Azure OpenShift / Kubernetes Security Review
09
E-Commerce and SaaS Platforms
10
Vulnerability Remediation Testing (Retest)
We follow published standards, Not a House Checklist.
From first call to signed off fix.
Six stages. You always know which one you are in. Nothing is tested without your sign off.
Scoping and rules of engagement
We agree targets, testing windows, contacts and what stays off limits. You have it in writing before anything is touched.
Week 0
Reconnaissance and mapping
We build the attack surface from the outside. Domains, hosts, technologies, leaked credentials and anything added without IT knowing.
Days 1–2
Manual testing and exploitation
Testers work by hand inside the agreed scope, joining small issues into the paths that matter. Anything critical is reported the day it is confirmed.
Days 3–7
Impact analysis
Each proven finding is rated on reach, business impact and effort to fix, so the order of work is defensible.
Day 8
Reporting and walkthrough
You get the technical report and the board summary, then a live session with the team doing the work.
Days 9–10
Retest and clearance letter
Once the fixes are in we retest every finding and issue a clearance letter for auditors, insurers or clients.
Within 90 days
In their words.
"Sadiq at AWJ Tech is an effective business partner. Throughout SHUAA's rapid business growth, he ensured world-class technology services in spite of constraints on available budget and headcount. He anticipates issues well in advance and provides timely recommendations. He has proven himself capable of rapid workarounds when the optimal best practice approach is not possible due to time, cost, and manpower limitations. "
– Stephen Stanton
SHUAA Capital (UAE)
"I have had the privilege of working with Sadiq Muhammad (from AWJ Tech). Sadiq's role as a Security leader whose expertise, vision, and leadership qualities resulted in the significant strengthening of our organisation's security posture. The team possesses expert security skills, broad and deep industry knowledge and in-depth understanding of regulatory requirements within the finance industry…”
– Ian Anderson
Hostplus (Australia)
"Sadiq is a dedicated, hard-working and thorough IT professional. He was proactive and well liked by our customers due to his 'can do' attitude. He plans and completes work without waiting to be prompted to do so. When faced with problems, proactively suggests solutions. Takes actions and decisions as appropriate to the business."
– Vijay C.
Emirates Airlines (UAE)
What clients ask us on every scoping call.
No. Denial of service is excluded unless you ask for it and sign it off. Testing windows are agreed in advance and we keep a contact reachable throughout. Anything that could affect availability is confirmed with you before it runs.
A vulnerability assessment is broad and mostly automated. It lists everything that looks weak. A penetration test is manual and narrow. A tester uses those weaknesses to show what an attacker could really do. Most companies need both. The assessment gives coverage, the test gives certainty.
It depends on the model. Black box testing needs almost nothing. Grey box testing needs a set of standard user credentials and returns more value for the same budget, which is why we usually recommend it. We will explain the trade off when we scope.
Yes, within the provider's rules. AWS, Azure and Google all allow you to test your own resources, and we handle any notice they require. Infrastructure that belongs to the provider stays out of scope.
In almost every case, yes. Our reports and clearance letters are written to support ISO 27001, PCI DSS 4.0 and NESA. We are happy to speak to your auditor or your client's security team if they need more detail.
You hear from us the same day. Critical findings go straight to your named contact with enough detail to contain the issue. We do not sit on an active risk until report day.